VAPT Services in Rajkot
Engineered for Growth
Mutant Technologies provides VAPT (vulnerability assessment and penetration testing) services in Rajkot, Gujarat. We test websites, web apps, APIs, mobile apps, servers and networks, report every weakness with steps to fix it, and re-test for free once the fixes are done. Testing follows OWASP methods, is aligned with CERT-In guidance and is covered by a signed NDA.
Trusted by ambitious founders, brands & modern businesses
Mutant Technologies provides VAPT services in Rajkot, Gujarat. We run vulnerability assessment and penetration testing on websites, web apps, APIs, mobile apps, servers and office networks, give you a clear report of every weakness we find with steps to fix it, and re-test for free once the fixes are done.
VAPT is a security check carried out the way an attacker would approach your systems, but with your permission and a written scope. The vulnerability assessment finds known weaknesses across everything in scope. The penetration test then tries to use those weaknesses, alone or chained together, to show what an attacker could actually reach. For a wider view of our security work, see our cyber security services.
What does a VAPT cover?
A VAPT is scoped around the systems you depend on. Most businesses start with what faces the internet, such as the website and customer portal, then add internal systems.
| What we test | What we look for | Typical example |
|---|---|---|
| Websites and web apps | Broken access control, injection, weak login and session handling, misconfiguration, from the OWASP Top 10:2025 list (OWASP) | A customer can open another customer's order by changing a number in the URL |
| APIs | Who can read or change which data, missing rate limits, data exposed in responses | A mobile app's API returns full customer records when only a name is needed |
| Mobile apps (Android and iOS) | Data stored on the phone, encryption, login, network traffic, tested against the OWASP MASVS (OWASP) | Login tokens saved in plain text on the device |
| External network | Open ports, exposed admin panels, outdated services, weak remote access | A database or remote desktop port open to the whole internet |
| Internal network | What an attacker could reach after getting into one office computer | Shared folders and ERP servers reachable from every machine |
| Cloud setup | Storage permissions, user roles, exposed keys and services | A storage bucket of invoices that anyone with the link can read |
We agree the scope in writing before anything starts: which systems, which addresses, which accounts, what is off limits and when testing happens.
Black box, grey box or white box?
The amount of information you give the tester changes what the test shows. We help you choose based on what you want to learn.
| Approach | What the tester gets | Best for |
|---|---|---|
| Black box | Only the website address or app, like an outside attacker | Seeing what a stranger on the internet could do |
| Grey box | Normal user accounts, sometimes basic documentation | Most business apps and portals; finds problems between user roles |
| White box | Accounts plus architecture details or source code | Deep checks before a major launch or for high-risk systems |
For most business apps and portals, grey box testing is a good place to start, because many serious problems only appear once you are logged in.
What's in your VAPT report?
The report is the part you keep, so we write it for two readers: the owner or manager who needs to make decisions, and the developer who needs to fix things.
- Management summary. In plain language: what was tested, the overall risk, the most serious findings and what to fix first.
- Scope and method. Exactly what was in and out of scope, the dates, the approach (black, grey or white box) and the standards followed.
- Findings. For each issue: where it is, how we confirmed it, its severity and business impact, and evidence such as screenshots or request details.
- Fix guidance. Specific steps for your developers or hosting provider, not just a generic link.
- Re-test results. After your team fixes the issues, we test again for free and update the report to show which findings are closed.
Every engagement is covered by a signed NDA and non-compete. Your systems, credentials and findings stay confidential.
Who needs VAPT in Rajkot and Gujarat?
Any business that holds customer data, takes payments online, or runs its sales or operations on software should test its security regularly. These are the businesses we most often talk to:
- Manufacturers and exporters in Rajkot, Shapar, Metoda, Morbi and Jamnagar whose overseas buyers send security questionnaires during supplier checks, or who run dealer portals and ERP systems that hold pricing and customer data.
- E-commerce and D2C brands, such as jewellery, fashion and food brands, that store customer addresses and phone numbers and accept online payments.
- Clinics, hospitals, schools and coaching institutes that keep personal records and need to show parents and patients that the data is protected.
- Software companies and startups in Rajkot and Ahmedabad preparing for a launch, a funding round or an enterprise customer's security review.
- Firms regulated by RBI or SEBI, who have audit requirements set by their regulator.
- Agencies that need an independent security check on a website or app they built for a client.
VAPT and compliance in India
Several rules make regular security testing a practical requirement, not just good practice.
CERT-In audit guidelines (2025). CERT-In issued its Comprehensive Cyber Security Audit Policy Guidelines on 25 July 2025. They say cybersecurity audits must be conducted at least annually, with more frequent audits where a sectoral regulator requires it (AZB & Partners). The same analysis notes that entities regulated by bodies such as RBI and SEBI must carry out mandatory audits through CERT-In empanelled auditors under their own frameworks.
Digital Personal Data Protection Act, 2023. Section 8(5) requires businesses to take "reasonable security safeguards" to prevent personal data breaches, and a breach of this duty can carry a penalty of up to ₹250 crore (Bar & Bench). A dated VAPT report with fixes and a re-test is one practical record of the safeguards you have taken.
PCI DSS for card payments. If you store, process or transmit card data, PCI DSS v4.0.1 asks for internal and external penetration tests at least once every 12 months and after any significant change, and for testing to be repeated to verify fixes (Strike).
If your regulator or customer specifically requires a CERT-In empanelled auditor, tell us at the start. We will tell you honestly whether our testing meets that requirement or whether you need a different route, before any work begins.
How to prepare for a VAPT
A little preparation makes testing faster and safer, and gives you a more useful report.
- Decide what matters most. List the systems that would hurt most if they were breached or went down.
- Choose live or staging. Testing a staging copy is safer for risky tests; testing live shows the real setup. Many tests use both.
- Create test accounts for each user role, such as customer, staff and admin, so access between roles can be checked.
- Tell your hosting provider or IT team about the test window, and allow our testing addresses if a firewall would block them.
- Take a fresh backup before testing starts.
- Name one contact person who can be reached quickly if testing finds something urgent.
Standards and tools we use
We follow the OWASP Web Security Testing Guide for websites and web apps, the OWASP Top 10:2025 for the most important web risks, the OWASP MASVS for mobile apps, and CERT-In guidance for reporting and logging. Our audits are OWASP and CERT-In aligned.
Tools include Burp Suite, Nmap, Metasploit, Wireshark and Kali Linux. Scanners find the obvious problems quickly; the findings that matter most, such as one user seeing another user's data, usually come from manual testing.
What our clients say
From our Google reviews:
"Excellent IT service! The team is highly skilled, responsive, and delivers solutions quickly. Truly impressed by their professionalism and support." — Ayyam Bhatti
"I’ve been associated with Mutant Technologies for quite some time, and they’ve never disappointed. Their service quality, quick response, and professional approach make them stand out. Truly a dependable team!" — Yagnik Viradiya
Cities we serve
Based in Rajkot. We work with businesses across Gujarat, including Ahmedabad, Surat, Vadodara, Jamnagar and Morbi, and with clients in 15+ countries.
Frequently asked questions
What is VAPT?
VAPT stands for vulnerability assessment and penetration testing. The assessment finds known weaknesses across your systems; the penetration test checks which of them an attacker could actually use and what they could reach.
How much does VAPT cost?
It depends on what is in scope: how many websites, apps, APIs or network addresses, how many user roles, whether it is black, grey or white box, and whether you need on-site work. Contact us with what you want tested and we will send a written quote.
How often should we do VAPT?
At least once a year, and again after major changes such as a new website, an app release, a new payment system or a server move. CERT-In's 2025 audit guidelines call for audits at least annually, and some regulators ask for more.
Will VAPT break my website or slow it down?
It shouldn't, if it is planned well. We agree the scope and timing with you first, avoid risky tests on live systems unless you approve them, and can test a staging copy instead.
Is the re-test free?
Yes. Once your team has fixed the reported issues, we test them again at no extra cost and update the report to show what is closed.
Are you CERT-In empanelled?
Our audits follow OWASP methods and are aligned with CERT-In guidance. If a regulator or customer requires a CERT-In empanelled auditor, tell us at the start and we will advise you honestly on the right route before any work begins.
Can you fix the problems you find?
Yes. Our web development and app development teams can fix the issues, or we can work with your own developers and explain each fix.
Related services
- Cyber Security: our full security service, including monitoring and staff training
- Website Development: secure, fast websites built in Next.js, WordPress and Shopify
- E-commerce Website Development in Rajkot: online stores built with payments and customer data in mind
- App Development: Android and iOS apps built with security in mind
- AI Automations: WhatsApp and CRM workflows that handle customer data carefully
Book a VAPT
Tell us what you want tested: a website, an app, an API, your servers or your office network. We will agree the scope, timing and report format with you before anything starts. Contact us or call +91 98798 46695.
Why choose us for VAPT Services in Rajkot?
Mutant Technologies provides VAPT (vulnerability assessment and penetration testing) services in Rajkot, Gujarat. We test websites, web apps, APIs, mobile apps, servers and networks, report every weakness with steps to fix it, and re-test for free once the fixes are done. Testing follows OWASP methods, is aligned with CERT-In guidance and is covered by a signed NDA.
Find It Before Attackers Do
Manual testing shows which weaknesses are really exploitable, not just a long scanner list.
A Report You Can Act On
Plain-language priorities for managers and exact fix steps for developers, plus proof of the re-test.
Confidential by Contract
Every engagement is covered by a signed NDA and non-compete before testing starts.

GoHighLevel (GHL), CRM Pipelines, Workflow Automation, Conditional Logic, Email & SMS Automation
GHL

The Beige Jewels
Web Development

SlideJewel
Web Development

SkySlope
Web Development
Efficient Process
Fast Results
Scope and NDA
We sign an NDA and non-compete and agree in writing what will be tested, when, with which accounts and what is off limits.
Vulnerability Assessment
Automated and manual checks across everything in scope to find known weaknesses and misconfigurations.
Penetration Testing
Manual testing that tries to use those weaknesses, alone or chained, to show what an attacker could actually reach.
"Mutant Technologies delivered on every promise. Their in-depth understanding of digital marketing has propelled our product to new heights."
What's included
Web App and API Testing
Manual and automated testing of websites, portals and APIs against the OWASP Top 10:2025, including access control between user roles.
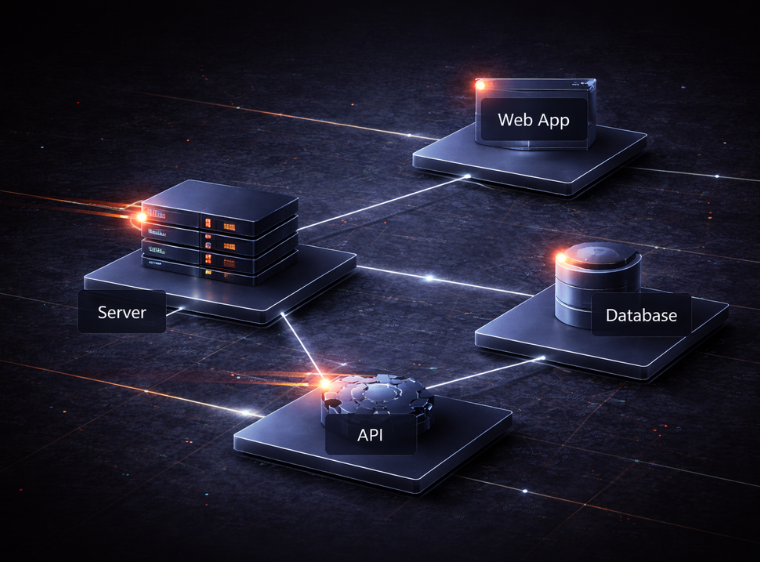
Mobile App Testing
Android and iOS apps tested against the OWASP MASVS: data stored on the phone, encryption, login and network traffic.
Network and Cloud Testing
External and internal network tests and cloud configuration checks for open ports, exposed services, weak access and leaked keys.
Clear Report and Free Re-test
A plain-language summary for managers, fix steps for developers, and a free re-test that confirms which issues are closed.
Complete Lifecycle
Scope and NDA
We sign an NDA and non-compete and agree in writing what will be tested, when, with which accounts and what is off limits.
Vulnerability Assessment
Automated and manual checks across everything in scope to find known weaknesses and misconfigurations.
Penetration Testing
Manual testing that tries to use those weaknesses, alone or chained, to show what an attacker could actually reach.
Report and Walkthrough
A management summary, findings rated by severity and business impact, and specific fix steps, explained on a call.
Free Re-test
Once your team has fixed the issues, we test again at no extra cost and update the report to show what is closed.
Ready to
Start?
Let's discuss your ideas and build something extraordinary together. Fill out the form, and we'll be in touch within 24 hours.
Fill out the form
Tell us about your project.
We get in touch
We'll schedule a discovery call.
Kickoff
We start building your vision.
Let's Build It
Tell us about your project and we'll craft the perfect solution.